Native analysisScanner finding
Preserve the analysis source and affected location.
SecurityVault is the enterprise security operating system: one graph of findings, policy and evidence from code to cloud. Scan source and images, check build dependencies, enforce deployment policy and assess running applications and cloud posture, every stage on one security context from the first commit to the running workload.
Illustrative sample scenario · Harbour checkout
Review the finding alongside the application, its environment and the responsible team.
A vulnerable dependency is one part of the story. The image carrying it, the workload running it and the team responsible determine the next questions to ask.
The shared ontology connects that context across SecurityVault’s capabilities. Security, engineering and audit teams work from the same relationships and evidence throughout the lifecycle.
Screenshots of the SecurityVault console from our own development tenant, captured on 1 November 2026 at 1280 px wide. Counts are live development data, not a customer environment. Journalists and analysts may reuse them with attribution.
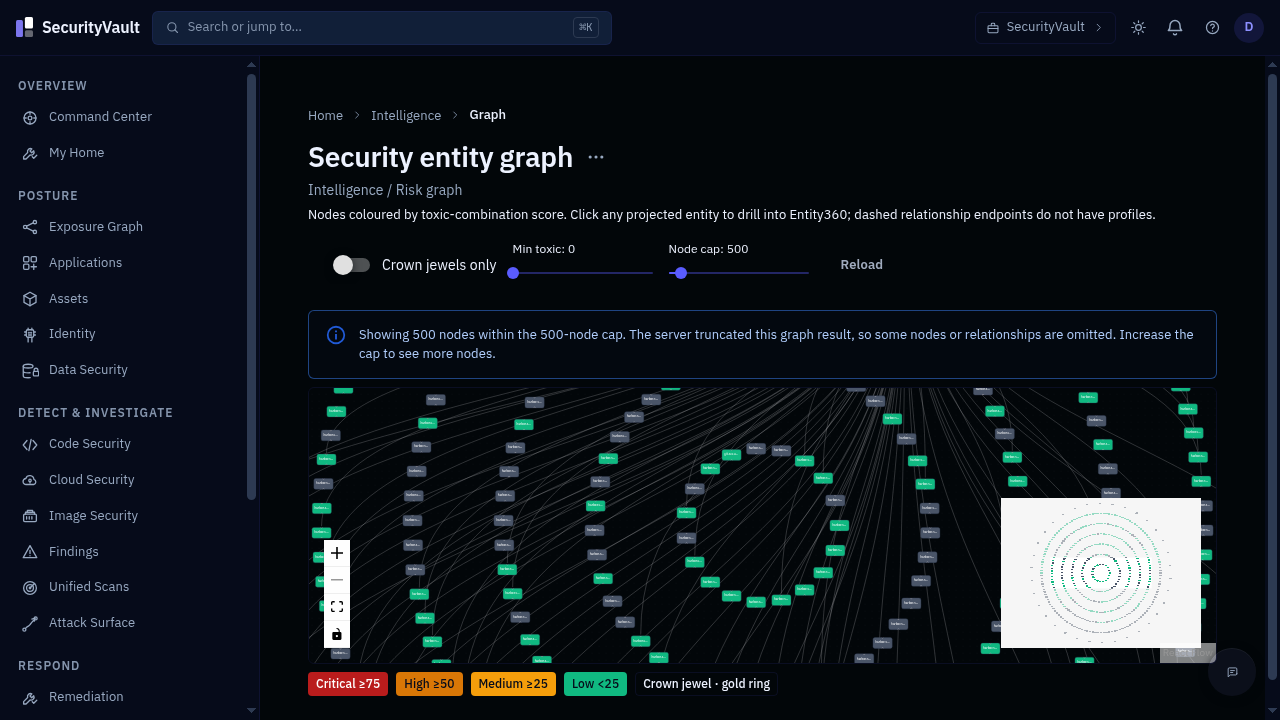
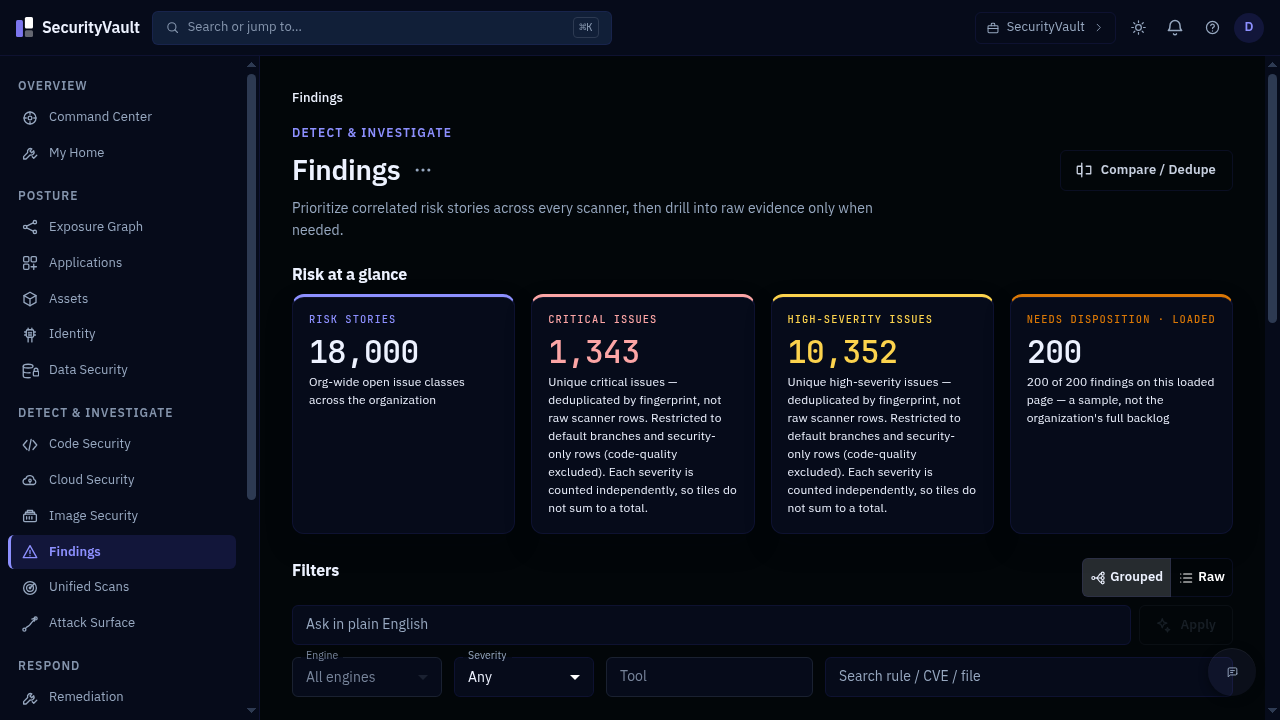
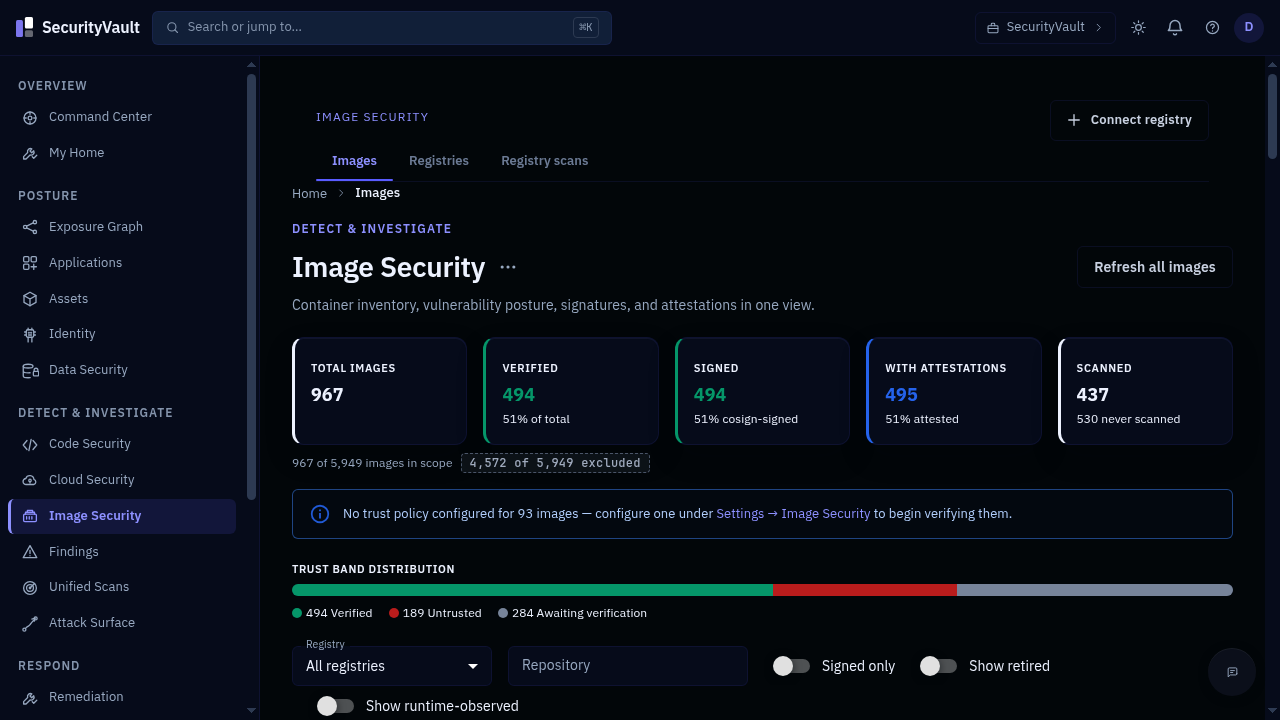
Inside the security engine
Each layer contributes to the same security engine and shared ontology. Explore the capabilities available today. Planned capabilities are listed separately.
Review source code, dependencies, secrets and infrastructure definitions before they become part of your running environment.
Connect the contents of a container image to its source and the workloads that run it.
Bring cloud configurations, identity permissions and Kubernetes posture into the same security investigation.
Coordinate remediation, evaluate release policy and retain evidence for security and compliance reviews.
Explore the workflow, then see it in a live demonstration with our engineers.
Illustrative sample scenario · Harbour checkout
01 / 04 · Investigate
Code to runtime
Investigate how source code becomes an artifact and where that artifact runs. Connections support the investigation; they do not replace review of the evidence.
Explore a fictional applicationsource.ref → build.ref
image.digest → workload.refReferences stay connected across the lifecycleRepository reference stays with the build.
The digest anchors the image to its provenance.
Follow the workload into its environment.
Follow the chain from a source change to a running service.
Application security
Native taint analysers cover 12 languages, alongside 45 scanner adapters. Analysis depth varies by language and tool; review the coverage that matters to your codebase.
Review SAST coverageCloud & runtime context
Review cloud posture, Kubernetes configurations and identity permissions alongside application findings. Runtime context here means workload and exposure relationships; planned detection capabilities are listed separately.
Explore cloud postureConnect your environment
Explore 29 registered connectors and the supported scanner adapters. Check each integration’s purpose and scope before planning an evaluation.
Evaluate with confidence
India is the initial hosting region. Expansion to the US and EU is planned around customer demand; those regions are not currently available.
Discuss residency, network and procurement requirements with our team before an evaluation. Detailed deployment requirements can be shared during your technical review.
Explore the workflows your organisation needs with a SecurityVault engineer. No repository access is required for an initial conversation.